IT Infrastructure That Helps Protect Your Organization
Consider how infrastructure itself can help protect, control, and recover critical workloads before deployment.
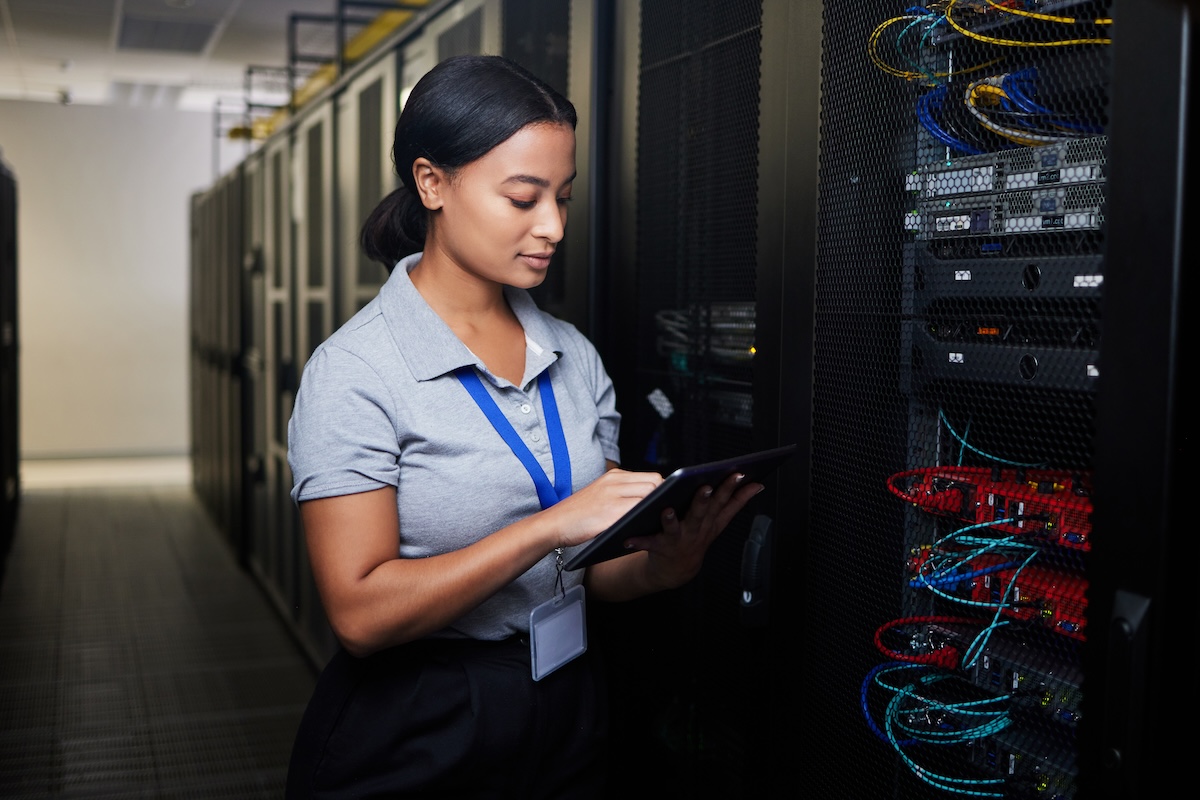
Cybersecurity has traditionally focused on the tools that protect an organization’s technology environment. Firewalls, endpoint security, identity management, and monitoring all play an important role, but they are only pieces of the puzzle. The hardware and infrastructure those technologies run on are part of the security strategy too. Servers, network equipment, edge devices, firmware, and management platforms connect to the systems organizations rely on every day. As workloads expand across data centers, cloud environments, and at the edge, securing that technology becomes an important part of managing risk.
Protection Starts with the Infrastructure
Security should be considered when infrastructure is selected, configured, and managed, not added as an afterthought. That means evaluating built-in hardware and firmware protections, securing administrative access, managing vulnerabilities throughout the technology lifecycle, and maintaining visibility across connected environments.
The network plays an important role as well. Secure network infrastructure can help organizations understand how users, devices, and workloads communicate while supporting controls such as segmentation and access policies. At the edge, those same considerations become increasingly important as technology moves into remote and distributed environments.
No infrastructure can prevent every threat, but resilient technology can help organizations contain incidents, maintain critical operations, and recover when something gets through.
Security isn’t limited to the software layer.
It extends across the infrastructure connecting and supporting the organization.
NEWCOM works with leading technology manufacturers across servers, networking, cybersecurity, connectivity, and edge technology to help organizations build and manage infrastructure with security in mind.
Did you know? NIST CSF 2.0 specifically addresses securing the hardware, software, services, and infrastructure that organizations rely on.

- Govern: The organization’s cybersecurity risk management strategy, expectations, and policy are established, communicated, and monitored.
- Identify: The organization’s current cybersecurity risks are understood.
- Protect: Safeguards to manage the organization’s cybersecurity risks are used.
- Detect: Possible cybersecurity attacks and compromises are found and analyzed.
- Respond: Actions regarding a detected cybersecurity incident are taken.
- Recover: Assets and operations affected by a cybersecurity incident are restored.
Did you know?
We hold several technology contracts you likely qualify for.
Are you looking to shorten the time from search to purchase of technology for your organization? Take advantage of a more streamlined buying process, with no need for Requests for Proposals (RFPs). All NEWCOM’s contracts have been awarded through the public bid process and are available in every state to meet your technology needs.

Request an Assessment with NEWCOM
NEWCOM is focused on safety and security. This includes securing mission critical data and systems. We represent leading manufacturers and software providers, such as CrowdStrike to focus on end-to-end cybersecurity solutions.
NEWCOM offers a comprehensive assessment, to reveal and give full visibility into potential risks associated with users and services for quick remediation. Upon completion, customers will receive a report outlining a summary of findings as well as a proposal of recommendations featuring CrowdStrike solutions that mitigate risks and shield their critical infrastructure from emerging cyber threats. Request an Assessment today at https://newcomglobal.com/